This guide explains how to structure and implement PeopleSoft Hhc in healthcare operations with a focus on governance, integration, and data quality. Background context clarifies what PeopleSoft represents in enterprise systems, what “HHC” typically signals in healthcare business processes, and why disciplined configuration matters for compliance, reporting, and lifecycle support.
“PeopleSoft Hhc” is a term that often comes up in healthcare systems discussions—not because it is a single vendor-defined product name with one universal feature set, but because teams use it to describe a healthcare-oriented PeopleSoft configuration and operating model. In other words, it typically refers to the way a PeopleSoft implementation is shaped to meet healthcare operational realities: patient-adjacent workflows, strict access controls, audit requirements, and finance/HR/procurement processes that must remain consistent and reconciled over time.
In healthcare operations, it is rarely enough that the application “works.” What matters is whether the organization can trust the data, enforce the right controls, and produce reliable reporting as workflows evolve due to regulatory shifts, organizational restructuring, and changing clinical/business needs. That is where PeopleSoft Hhc tends to matter: it emphasizes governance, integration discipline, and audit-ready output—dimensions that become critical in regulated or high-accountability environments.
From an industry-expert standpoint, the most important question is not simply, “Can PeopleSoft be installed and configured?” but rather, “Can it be governed so that data remains consistent, controls remain auditable, and reporting stays reliable as processes change?” A PeopleSoft Hhc approach is usually evaluated against outcomes such as:
Operational trust is the underlying theme. When PeopleSoft Hhc initiatives succeed, it is because teams align business owners, IT architects, security leads, and analytics stakeholders around a shared set of requirements and measurable acceptance criteria. That alignment reduces rework during testing, prevents fragile or ambiguous integrations, and ensures downstream decisions—like operational forecasting and compliance reporting—are grounded in trusted data rather than “best-guess” reconciliation or tribal knowledge.
To understand “PeopleSoft Hhc,” it helps to interpret the term as an implementation orientation rather than a single bounded product. “PeopleSoft” refers to a mature enterprise suite used for core operational management—commonly including finance, procurement, human resources, and related administrative and transactional capabilities. Organizations use it to run processes that require consistent master data, policy-driven workflows, and controlled changes over time.
“Hhc” is frequently used as a shorthand for a healthcare-related environment—such as a healthcare entity, service line, operational model, or specific healthcare industry scenario. In practice, “Hhc” implies there are additional constraints beyond typical ERP deployments. These constraints may include healthcare governance requirements, stronger segregation-of-duties expectations, specialized audit evidence needs, and integration relationships with identity management, clinical-adjacent systems, financial tooling, and reporting warehouses.
Because PeopleSoft covers broad operational domains—finance, procurement, and HR administration as well as workflow capabilities—a PeopleSoft Hhc approach usually focuses on how those domains behave together in a healthcare context. That often includes:
An expert view of implementation risk typically ties to two things: (1) configuration complexity and (2) data integrity. Healthcare operations often cross organizational timelines and departmental ownership boundaries. Even if an application is configured correctly at launch, risk can arise if the operating model does not keep data consistent as new workflows, new units, or new compliance requirements are introduced.
Another practical dimension is organizational intent. Some programs use PeopleSoft Hhc to consolidate operations and reduce duplication of processes and master data across systems. Others use it as a stabilizing layer for financial and workforce governance, keeping operations auditable and reportable. The meaning of “PeopleSoft Hhc” therefore depends on what the organization aims to achieve—consolidation, governance, standardization, or improved auditability—and on the complexity of integrations with surrounding healthcare technology.
When advising teams on PeopleSoft Hhc initiatives, it is useful to use the “inverted pyramid” approach: prioritize the highest-impact items first, because small failures early in the program tend to cascade into costlier remediation later. In a healthcare-adjacent PeopleSoft program, the top priorities are usually those that establish trust, enforce controls, and preserve consistency.
Healthcare organizations often face “silent drift,” where configurations change over time without adequate traceability, documentation, or evidence. In such environments, PeopleSoft Hhc becomes fragile: it may appear stable, but changes accumulate, and the system slowly diverges from intended governance or from what business owners believe is “how it should work.” When audits arrive or when reporting becomes inconsistent, the organization discovers that it cannot explain why outputs changed.
A strong governance model for PeopleSoft Hhc typically includes:
Governance is not only a process; it is also a set of practical mechanisms. For example, many high-performing programs establish a configuration registry (what was changed, where, why, and by whom). They also define acceptance criteria that are measurable, such as “approval events must generate an audit record with timestamp and user identity” or “reporting metric X must match reconciled totals within defined tolerance ranges.”
PeopleSoft Hhc deployments frequently rely on interfaces to other healthcare systems. These might include identity and access systems, HR/credential sources, financial tooling, master data services, reporting data pipelines, or domain-specific applications (for example, vendor and procurement ecosystems). The primary failure mode is often not “connectivity”; it is data mismatch.
When integration payloads are ambiguous or when systems interpret the same fields differently, downstream reports can become unreliable. Even small inconsistencies—like formatting differences in identifiers, mismatched status codes, or missing mandatory fields—can undermine operational trust.
To reduce integration-related risk, teams should establish:
An expert integration program also includes monitoring that is aligned to operational outcomes. For example, monitoring should detect not just “messages delivered,” but “messages accepted and validated.” It should capture business-level error metrics, such as the percentage of transactions rejected due to validation rules, the volume of records requiring manual correction, and the time-to-resolution for integration failures.
In healthcare-adjacent operations, audit trails and access control are not optional. Even when healthcare systems do not directly store clinical content in PeopleSoft, PeopleSoft often hosts operational and financial data whose handling still requires compliance-grade accountability.
For PeopleSoft Hhc, security design should be built around job roles and responsibilities. Teams should implement least-privilege access, but must also validate that segregation-of-duties requirements are preserved. “Least privilege” is not enough if users can bypass controls through role combinations or if audit logs become incomplete due to misconfigured logging levels.
Security should be tested with realistic scenarios, including:
Audit-readiness extends beyond access control. It includes the ability to trace who changed what, when, and why. It also includes the retention and accessibility of audit evidence. In a mature PeopleSoft Hhc program, audit evidence is treated as a production deliverable—something stakeholders can rely on to answer auditor questions quickly without hunting through logs or spreadsheets.
Leadership often needs dependable operational views: dashboards for performance, oversight reports for compliance, and extracts for finance and audit functions. With PeopleSoft Hhc, reporting reliability depends on consistent data definitions, stable transformation logic, and documented metric logic.
A frequent problem in ERP and operational suites is that teams build reports using locally understood assumptions that are not documented as business definitions. Over time, as additional departments contribute data, those assumptions diverge. PeopleSoft Hhc mitigates this risk by emphasizing stable definitions of:
Reporting logic should be treated as governed business logic, not a technical convenience. Expert teams document each metric, define authoritative source fields, and validate report outputs against reconciled totals. They also establish change control for report definitions so that new reporting requests do not silently alter existing metrics without stakeholder notification.
Even if there is no single “standard” PeopleSoft Hhc blueprint, successful programs often share certain design patterns. These patterns help teams maintain clarity across configuration, testing, support, and lifecycle management.
The value of patterns is that they reduce ambiguity and help teams scale. In healthcare operations, where departments and governance complexity can increase quickly, patterns help ensure the implementation remains coherent and understandable long after go-live.
Healthcare enterprises frequently maintain overlapping datasets across systems. Identity may live in one system, organizational structure in another, and financial hierarchy in yet another. For PeopleSoft Hhc, you generally want to identify which system is authoritative for each domain. The objective is not to eliminate all integration complexity—many organizations must integrate anyway—but to prevent contradictions.
Common “single source of truth” decisions include:
Once authoritative sources are set, integration and reporting should reflect the decision consistently. This is critical for reconciliation and auditability. If multiple systems are treated as “authoritative” for the same attribute, discrepancies are guaranteed—sometimes only discovered after audits or operational incidents.
Instead of configuring screens and fields first, expert teams map role-based workflows first. They identify:
This mapping drives configuration priorities and test case design. It also clarifies segregation-of-duties and ensures the security model supports the operational reality.
Role-based mapping is particularly important in healthcare contexts where oversights and approvals might be more stringent. For example, procurement approvals might require different authority levels depending on funding source, organizational unit, and dollar thresholds. Similarly, HR workflows might need approvals linked to credentialing status or department oversight.
Healthcare organizations are dynamic. Reorganizations happen. Policy controls change. Reporting requirements evolve. PeopleSoft Hhc configuration should be prepared for controlled changes so that updates do not cause regressions across dependent workflows.
Building for lifecycle change usually involves:
It also involves designing with effective dating and organizational changes in mind. Many operational metrics depend on effective-dated hierarchies. If configuration does not handle reclassifications or historical interpretations properly, reporting results can change unexpectedly or become inconsistent across time.
PeopleSoft sits within the broader enterprise application landscape: ERP systems and operational suites that manage finance, workforce administration, procurement, and related operational controls. In healthcare organizations, these systems are used not only for transactions but also for governance, audit evidence, and reporting.
While PeopleSoft implementation details vary based on scope and organizational strategy, the governing concepts remain consistent across regulated or high-accountability industries:
When teams search for broader enterprise guidance, they often consult recognized frameworks and research institutions. For example:
These sources are useful for program-level guidance, but organizations should still validate specific quantitative claims and technical assertions. Any numerical performance claims about PeopleSoft behavior, integration throughput, or audit log retention should be verified against current vendor documentation, peer-reviewed research, or internal pilot metrics. Because scope and integration complexity vary widely, case study results should be assessed in context.
In practice, “reliable sources” for PeopleSoft Hhc programs often include:
That combination helps teams avoid the trap of adopting generic best practices that do not align with healthcare-specific oversight expectations or with the organization’s actual data flows.
The steps below reflect a conservative, audit-aware approach commonly recommended for enterprise healthcare implementations. While many organizations adjust sequencing to match governance, release cadence, and internal resource availability, the core logic remains: establish requirements and governance early, design data and security with rigor, validate integrations and reporting before go-live, then stabilize with disciplined post go-live operations.
Start by documenting which healthcare-related processes are included in PeopleSoft Hhc. Scope definition should be specific enough to support configuration and test planning. Examples of in-scope areas often include finance-driven controls, procurement governance, workforce workflows, and reporting outputs required for operational oversight.
Equally important is defining what is explicitly out of scope. Out-of-scope items should be documented to prevent uncontrolled scope expansion. Healthcare programs sometimes drift because stakeholders discover adjacent needs during workshops. Without explicit boundaries, “just one more workflow” can become a major effort that affects integrations, testing, and release readiness.
Map current workflows to PeopleSoft capabilities. Identify gaps that require configuration, integration development, or—where appropriate—process redesign. Produce a fit-gap matrix and obtain sign-off from business owners and other stakeholders responsible for the affected domains.
A mature fit-gap assessment also identifies “workarounds” used in today’s environment and evaluates whether those workarounds should be eliminated. For example, if the current process relies on manual spreadsheets for reconciliation, the fit-gap assessment should determine whether PeopleSoft can provide a governed alternative. If it cannot, the organization must decide whether the workaround remains temporary or becomes a permanent operational pattern.
Define authoritative sources and data stewardship responsibilities. Master data governance is a major determinant of operational trust. It includes decisions about:
Create a data quality plan that includes validation rules, exception handling procedures, and reconciliation expectations. The plan should also define measurement: what thresholds define “acceptable quality” and how quality issues are tracked to closure. In healthcare operations, manual reconciliation is expensive and increases audit risk. A robust PeopleSoft Hhc program aims to reduce manual corrections by improving governance and validation logic.
Security design should begin early. Define roles, permissions, and segregation-of-duties needs based on operational responsibilities. Validate audit trail requirements: what evidence must be captured to satisfy audit needs and compliance expectations.
Then test security with realistic scenarios. This means testing not only standard user journeys but also operational edge cases. Examples include:
During these tests, validate both functional outcomes and audit evidence. For example, if an approval is rejected, the audit trail should still show the rejection event with appropriate user identity and timestamps. If a user is denied access, the system should produce consistent log entries useful for troubleshooting and audit.
Define integration points and data contracts. Implement unit tests for transformation logic and run end-to-end test cycles that include error and retry cases. In a PeopleSoft Hhc context, it is crucial that integration tests validate business semantics, not just technical delivery.
For example, if an incoming record sets a status to “approved,” the receiving system should interpret that correctly based on its configured codes and workflow states. Validation should check not only whether a field is present, but whether the field value is meaningful in the context of PeopleSoft configuration.
A high-quality integration testing strategy often includes:
Build reporting definitions early enough to test data consistency. Document each metric’s business logic so that stakeholders trust results and support teams can maintain them over time.
In PeopleSoft Hhc deployments, reporting often includes operational oversight and governance reporting. That reporting should:
Document metrics and ensure changes are governed. If a metric definition needs improvement, the organization should manage versioning and communicate impact. This prevents “silent” metric drift that can undermine leadership trust and complicate audits.
Run test cycles that include operational edge cases: reclassifications, late approvals, partial data, and exception workflows. Confirm that monitoring, incident response, and support procedures are ready before go-live.
Operational readiness should include:
In healthcare operations, operational readiness also includes stakeholder training and support for users who may have heightened oversight responsibilities.
Prefer phased rollout where feasible. Maintain a release plan aligned with organizational adoption and training, and track issues through a structured triage process.
Phased rollout reduces operational disruption by limiting exposure. It also helps teams learn and stabilize. However, to avoid user process drift across phases, training and playbooks must be consistent. Otherwise, early adopters may develop workarounds that later become difficult to remove.
In the months after go-live, focus on refining workflows, improving data quality, and tuning integrations. Use operational metrics and business feedback to prioritize enhancements.
Post go-live stabilization should measure outcomes such as:
Most importantly, maintain disciplined change control. PeopleSoft Hhc programs can regress if quick fixes are applied without governance. A structured enhancement backlog and release planning helps ensure the system evolves without losing control.
The table below compares common PeopleSoft Hhc implementation approaches. It clarifies typical trade-offs and requirements organizations should validate internally. This is not a pricing statement; it is a risk-and-requirement framing to support program planning.
| Approach | Top for | Primary source of risk | Conditions / Requirements |
|---|---|---|---|
| Standardized configuration with controlled extensions | Organizations aiming for predictable upgrades and lower complexity | Business fit gaps if workflows are not carefully mapped | Clear fit-gap documentation; disciplined configuration governance; acceptance criteria signed by business owners |
| Heavier customization for healthcare-specific workflows | Environments with unique operational policies | Regression risk and good maintenance burden | Strong test automation; documented customization inventory; release impact analysis before changes |
| Integration-first with robust data contracts | Organizations with complex interfaces to operational systems | Data mismatch and reconciliation gaps | Data contract standards; reconciliation routines; defined error handling and monitoring SLAs |
| Phased rollout with targeted training | Organizations that need adoption control and reduced operational disruption | User process drift and inconsistent behavior across phases | Training readiness; playbooks; change control with feedback loops; measurable adoption KPIs |
In many successful PeopleSoft Hhc programs, the “best” approach is rarely one of these options in isolation. Instead, organizations blend approaches. For instance, a program might use standardized configuration as a baseline, apply controlled extensions only where essential, implement integration-first data contracts for the most critical interfaces, and then execute phased rollout to reduce disruption. The key is that the governance model and acceptance criteria remain consistent throughout these blended strategies.
You have not provided specific numeric prices, supplier names, or a city/country. In PeopleSoft Hhc programs, “price” is typically influenced by scope (number of modules/workflows), integration complexity, data migration effort, security and reporting demands, and release timeline. Even when price appears comparable across vendors, the true cost of delivery often differs based on risk management maturity and the ability to maintain stable releases.
Accordingly, expert procurement and program teams validate these items before committing:
If your organization is a public sector entity, an integrated delivery network, or a private provider, requirements for audit evidence, documentation expectations, and governance processes may differ. The supplier should be able to demonstrate a delivery approach aligned to those requirements. Location can matter in practical ways—availability of specialized PeopleSoft staff, time zone coordination for integrations, and local compliance expectations—but it is rarely the dominant factor compared to scope, risk management, and integration complexity.
If you share your target organization type (public sector, private provider, integrated delivery network) and your intended PeopleSoft Hhc scope, the evaluation checklist can be made more precise for supplier selection and cost validation. For now, a generic but rigorous approach is to require bidders to describe:
For PeopleSoft Hhc, delivery teams typically need the following conditions satisfied to avoid common pitfalls. Many of these conditions are organizational readiness factors rather than purely technical requirements.
Where these conditions fail, the consequences often appear later as rework. For example, inadequate data governance can cause reporting discrepancies that lead to prolonged testing cycles and stakeholder frustration. Insufficient security design can produce audit gaps that require emergency fixes before go-live. Inconsistent change management can create “configuration archaeology,” where teams cannot identify why system behavior changed after a release.
To reduce these risks, PeopleSoft Hhc programs often establish a delivery cadence with frequent demos, stakeholder feedback loops, and evidence-based progress checks. Rather than relying solely on schedule milestones, they focus on validated readiness artifacts: approved requirements, signed-off fit-gap matrices, data contract documentation, security role matrices, test coverage reports, and reconciliation evidence.
“PeopleSoft” refers to the enterprise software suite, while “Hhc” is commonly used to denote a healthcare-oriented organizational configuration or implementation context. The exact meaning depends on the adopting organization’s internal naming conventions and scope. In practice, it usually implies healthcare-grade governance, audit-readiness, security controls, and integration discipline shaped around healthcare operational processes.
Often, yes. Many organizations aim to use standardized configuration first and then add controlled extensions only where business workflows truly require it. The key is a rigorous fit-gap assessment and well-defined acceptance criteria. Teams should also evaluate whether “customization” is truly necessary or whether process adjustments can meet operational requirements with lower long-term maintenance burden.
Integrations heavily influence data consistency and reporting reliability. If interfaces deliver inconsistent identifiers, conflicting status codes, or incomplete payloads, then PeopleSoft Hhc outputs—especially reporting—can become unreliable. Using clear data contracts, robust end-to-end testing (including reconciliation), and strong monitoring reduces failures and ensures operational reports remain trustworthy.
A role-based access model aligned to job responsibilities, supported by least-privilege permissions and tested audit trail behavior, tends to work best. You also want procedures for temporary access and role reassignments so the security posture remains stable as personnel and responsibilities change.
Testing should cover end-to-end workflows, data validation rules, authorization/approval paths, reporting extracts, and integration error scenarios. Expert teams also verify regression impact for any configuration changes. In healthcare-adjacent contexts, testing should include operational edge cases that reflect real-world timing and exception handling (late approvals, partial data, reclassifications, and workflow reversals where allowed).
Start with documented metric logic and stable data definitions. Build reports early enough to test end-to-end data flows, and confirm that stakeholders agree on business logic before go-live. Reporting reliability improves when metrics are treated as governed business logic with controlled changes and validated outputs against agreed reference totals.
Teams often rely on official vendor documentation, recognized security and risk frameworks (such as NIST), and research guidance from established industry analysts (such as Gartner). Your organization should also validate any quantitative claims using internal pilot metrics or verified case studies relevant to your scope. For PeopleSoft Hhc, internal audit requirements and governance expectations are equally important sources of guidance.
PeopleSoft Hhc is best approached as a systems-and-governance initiative, not just a technical deployment. When healthcare organizations emphasize requirement clarity, disciplined configuration, secure access controls, and integration contracts, the result is not merely “a system that runs.” It becomes an operational backbone that supports auditability, consistent reporting, and sustainable lifecycle management.
The deeper value of a PeopleSoft Hhc approach is trust—trust that approvals are enforceable and traceable, trust that data is consistent across systems, trust that reporting metrics match business definitions, and trust that audits can be answered with evidence rather than speculation. Those outcomes are achieved through deliberate choices: governance early, data contracts for integration, role-based security aligned to responsibilities, and reporting logic treated as governed business logic.
If you want to move from general guidance to a tailored plan, share your PeopleSoft Hhc scope (modules/processes involved, main integrations, reporting needs, and any known compliance or audit constraints). With that information, it becomes possible to tailor the step-by-step plan, prioritize testing and reconciliation, and define a security and reporting approach that matches your operational reality.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Finding an optimal mix of insurance premiums and direct medical costs is crucial for effective healthcare budgeting. This discussion will delve into tactics to achieve a balance that aligns with your finances.
4rkojvsx Technology: Industry Insights and Buying Guide
This guide explains 4rkojvsx with an evidence-based, step-by-step approach to evaluating suppliers, pricing, and requirements before purchasing. Objectively, the term points to a technical category where compatibility, quality controls, and documentation matter as much as the nominal price. Readers will also find a practical comparison table, conditions, and targeted FAQs.
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Selecting an adept dentist is critical for ensuring the efficacy and your satisfaction during a dental implant procedure. This in-depth guide is designed to assist you in finding a dental expert who meets your personal requirements, guaranteeing that your path to dental implant success is seamless and fruitful.
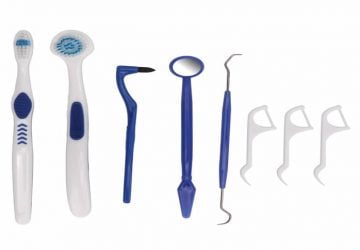
Protect Your Perfect Smile: Master the Art of Defending Your Teeth Against Acid Attacks
Though they may tantalize the palate and invigorate the senses, foods and drinks with high acid content are a double-edged sword with regard to oral wellness. Continual exposure to these substances progressively strips away the protective enamel from our teeth, which can lead to increased sensitivity, changes in coloration, and a variety of other dental complications. This composition offers insight into relishing these zesty favorites while safeguarding your teeth from damage.
Comprehensive Insight into Boob Enhancement
Boob enhancement is a cosmetic procedure aimed at augmenting the size and improving the shape of breasts for aesthetic purposes. With the evolution of medical procedures, this enhancement has become more sophisticated, offering various options to cater to individual preferences and needs. This detailed guide explores the intricacies of boob enhancement, tackling myths, benefits, and expert advice to help potential candidates make informed decisions.
Pmoc Abrava: Supply, Pricing, and Quality Guide
This guide explains what “Pmoc Abrava” is used for in professional settings and how suppliers evaluate quality and consistency. It offers an objective overview of common procurement considerations, documentation, and verification practices. Readers will also find a comparison-style supplement section and practical requirements before choosing a source.