This guide explains how email login workflows operate and why verifying access security matters. Objectively, “[email protected]” appears to be an email-login identifier string. Such strings are commonly used in account-access contexts, but they can also be misused in phishing attempts if handled carelessly, especially when authentication steps are unclear or repeated.
When you encounter an identifier like [email protected], the very important practical step is to handle it as potentially sensitive. Even if the string appears to be “just text,” it can function as an authentication-related artifact in real-world workflows. Email login workflows—whether for personal inboxes, enterprise systems, support portals, HR tools, or billing platforms—depend on authentication signals that should never be shared in insecure channels, and should not be typed into unknown forms.
In professional security practice, the goal is often described in simple terms, but executed with rigor: ensure the authentication path is legitimate, encrypted, and bound to the correct account context. That means you should not treat “a string that looks like an email” as harmless. Instead, treat it like something that could be linked to a specific account. If an attacker can connect your identity to an authentication flow—even indirectly—they may use it to improve a phishing pretext, craft a more convincing impersonation attempt, or narrow down where to target you.
In other words, the string is not necessarily a secret in the way a password is secret, but it can still be a valuable piece of information for attackers. Security teams categorize this kind of data as sensitive because it can reduce uncertainty for the adversary. It can help them write messages that appear customized (“we have an account status issue for Maria…”), and it can help them craft instructions that mirror the real provider’s language and formatting.
As a practical habit, whenever you see an identifier that appears tied to login or account access, ask yourself: “Where did I see this, and what is the safest place to complete authentication?” The safest place is almost always the official provider interface that you reach by typing the known domain yourself or by using a trusted bookmark you control—not by filling forms on pages that might be attacker-hosted.
Strings such as [email protected] often resemble concatenated text that could be associated with login screens, account recovery notes, internal identifiers, or system-generated labels. However, email authentication systems generally rely on well-defined fields (e.g., the mailbox address and a password, plus optional second-factor verification). If a user interface or message presents an unconventional “combined” identifier (for example, a word plus domain plus “.login”), it can be a sign of:
From an industry perspective, the risk is not the presence of the characters—it’s the context in which they are used. Authentication systems and secure UI flows have consistent patterns. Users are trained (often implicitly) that the login form asks for an email address (or username), not a combined label. If the UI looks different from expected, it can create confusion. Attackers exploit confusion. They use formatting that “feels” technical or system-like to reduce suspicion.
Security teams look for mismatch between the user’s expected flow and the flow being requested. For example:
Therefore, exact formatting matters because it shapes what a user thinks is being requested. When a message includes “.login,” the user might infer that it’s a special login username format used by the provider. If they believe that, they might type the string into the provider login field. If that field expects only an address, the user may still enter it—especially if the attacker designed the page to accept it and proceed—creating an opportunity for credential theft.
Even if the attacker’s page doesn’t work perfectly, phishing often succeeds on imperfect conditions: users type something, the system responds, and the attacker harvests the credentials. The attacker’s goal is not always to create a perfect technical mimicry. It’s to convince you to do the one action they need: provide access. Misformatted identifiers are one of the tools they use to move you toward that action.
Very modern email services follow a similar high-level authentication pattern. While the exact UI can differ between providers, the logic tends to remain consistent because it must work securely under many conditions (global access, device differences, risk scoring, and regulatory requirements). A simplified view looks like this:
When a workflow deviates from this pattern—especially when it directs users to enter credentials into pages that are not clearly legitimate—security posture deteriorates rapidly. Attackers frequently exploit deviation. They might:
In many legitimate systems, the login flow begins with a known provider domain and uses standard TLS-protected pages. The user’s browser shows a certificate that matches the provider’s domain. If you are sent to a page that doesn’t match that expectation, you should treat it as untrusted.
Professional practice also emphasizes that users should not “bootstrap trust” based on a message’s tone. A message can be urgent, technical, and well formatted, yet still be malicious. Security requires consistent authentication pathways that users can recognize: official entry points, consistent domain names, and predictable MFA prompts.
In practice, the most concerning scenario is when someone receives a message that includes or references something like [email protected] and is prompted to “log in now” through a form. Attackers often use convincing formatting to make the request feel operationally necessary. They may claim:
Even without clicking a link, users may be tempted to “try just this once.” This temptation is extremely important in phishing modeling: attackers assume that humans will prefer resolution over caution. They often craft the message so that the “login string” looks like the correct input for the login prompt. The user sees it as a clue: “Here is my login identifier; I just need to confirm it.”
Security researchers and standards bodies generally emphasize that phishing success depends on user action, not technical sophistication alone. Attackers can invest in social engineering because it scales with behavior. If an attacker can cause you to type credentials into their page, the game is over.
Professional mitigation therefore focuses on verification habits. You verify:
Where “login strings” become dangerous is when they are used as bait. The attacker wants you to believe that the string is safe because it “comes from your account.” But attackers frequently know your email address—data that can be public, leaked, or obtained through other means. Knowledge of the address is not proof of legitimacy. It is only proof that the attacker knows enough to sound credible.
Additionally, attackers use patterns like “.login” to create an illusion that the value is part of the provider’s infrastructure, rather than a random label. Users may think the provider uses a custom username format. That mistaken belief is the vulnerability.
To keep authentication safe, experts typically apply practical conditions—especially in regions where consumer and small-business email accounts are widely used for billing, HR coordination, customer support, and day-to-day operations. In Brazil and similar contexts, email is often a central hub. That makes phishing more damaging because compromised email can lead to:
Accordingly, experts advise a baseline set of safe behaviors. For your daily routine, these conditions work well:
It’s also wise to adopt an organizational habit: when a login prompt arrives unexpectedly, treat it as suspicious until proven otherwise. Legitimate providers and legitimate IT processes have ways to communicate securely (for example, official status pages, known helpdesk systems, and consistent ticket flows). An urgent email message is not a secure communication channel for credential collection.
In many real security incidents, the breach starts with a small behavior deviation. A user receives a message with a “login identifier,” clicks, types the credentials, and proceeds. The technical attack might be simple, but the impact is huge. The conditions above help prevent the first step.
You asked for price information and supplier details to be integrated, but no specific price, supplier name, or vendor dataset was provided in the input. In a professional environment, an expert approach is to avoid fabricating costs. Instead, you should confirm the exact vendor or service category involved (for example, email hosting, identity management, managed MFA deployment, endpoint security, or anti-phishing training), then request a written quote or check an official pricing page from the provider directly.
In security and identity projects, “login” is rarely just a UI issue. It usually ties into broader systems: identity providers (IdPs), single sign-on (SSO), conditional access, and secure session management. Therefore, any supplier claim about “fixing login access” must be evaluated in terms of how they change authentication flows and what data they request.
If your goal is account access tooling—such as identity verification services, managed MFA deployment, or enterprise email security—costs usually depend on multiple factors. Rather than guessing numbers, verify what applies to your situation:
Because the user request mentions integrating supplier context, it’s useful to apply a supplier vetting lens specifically to “login help” providers. A vendor that asks for passwords (or requests credentials during troubleshooting) is a red flag. Legitimate support will generally never require you to share the password of an email account. Instead, they may request access through secure administrative channels or through revocation/re-auth steps performed on your behalf within the provider’s own management tools.
Practical recommendation: treat any “login help” supplier claiming to solve access issues as a vendor that must be vetted. Ask for a purchase order or contract, verify company identity (legal name, address, and registration), verify what access they will request (read-only logs vs. administrative actions), and ensure they do not request passwords during troubleshooting. If they claim to need passwords, consider that an immediate stopping point.
Additionally, for organizations in Brazil, confirm whether the supplier offers compliance-aligned handling of personal data under applicable data protection requirements. Even if you are not a large enterprise, strong vendor governance is beneficial because identity systems often handle personal data in logs and user profile attributes.
To support real-world decisions around login identifiers, the comparison below frames common scenarios and requirements. It does not assume any particular provider and avoids sharing any real credential data. Instead, it focuses on decision criteria that help you choose safe actions.
| Scenario | Top-Case Interpretation | Risk Level | Source/Trigger | Step-by-Step Check | Requirements/Conditions |
|---|---|---|---|---|---|
| Identifier appears in a personal note | Unstructured labeling or copy-paste artifact | Low | Your own saved message or document | Verify the mailbox address separately; open the provider site manually; attempt login only on the known official interface. | Access only via trusted devices; never share the full identifier in public or third-party forms. |
| Identifier appears in an email you didn’t request | May be spoofing or phishing bait | High | Unexpected message asking for login action | Check sender domain; do not enter credentials from the message; navigate to the provider directly; verify MFA prompts are expected. | MFA enabled; domain validation; avoid “urgent” instructions without verification. |
| Identifier appears in a company helpdesk chat | Internal workflow reference | Medium | Support context | Confirm the support channel authenticity; ask what exact step they need you to perform; ensure they do not request passwords. | Support staff use secure ticketing; no credential collection by support. |
| Identifier appears on a third-party page | Could be legitimate app integration | Unknown/Varies | Web form requesting credentials | Inspect domain; verify certificate; confirm the integration uses standard OAuth-like flows; avoid forms requesting raw passwords. | Use official integrations; require clear consent and redirect behavior consistent with industry norms. |
If you’re trying to understand or resolve an access confusion involving a string like [email protected], a careful verification workflow reduces the chance of compromise. The key is to slow down long enough to verify the flow and domain before taking any action that could expose credentials.
In Portuguese-speaking business settings—where shared inboxes, HR requests, invoice approvals, customer support, and procurement communications are often routed through email—operational habits matter as much as technology. A common cultural pattern is to rely on fast messaging to “resolve faster.” That speed is valuable for productivity, but it can undermine security if it bypasses verification steps.
For security, experts advise formalizing a baseline that applies to every department. Below are common requirements that organizations often implement, adapted to the realities of email-driven workflows in Brazil:
It’s also helpful to build a “verification ritual” for staff. For example: when a user sees a login request, they should not respond inside the channel; they should navigate to the provider site themselves. Similarly, when staff receive messages requesting re-authentication, they should check whether the message matches known internal processes or whether it could be external phishing.
Another operational note: local businesses sometimes use WhatsApp extensively. Attackers exploit that by bridging email compromise into messaging impersonation (“I’m stuck, check this code”). Organizations should train employees that a login code (OTP) must not be shared via chat. If a code arrives, the user uses it only within the legitimate provider interface.
In practice, if you treat login identifiers as sensitive data and create consistent procedures, you reduce both accidental compromise and social engineering impact. Attackers become less effective because the organization’s responses are predictable, controlled, and auditable.
It likely represents a concatenation of an email-like identifier and a label indicating a login-related context. In normal security practice, the mailbox address and login action are separate concepts; unusual formatting can sometimes be benign (copy-paste) but can also appear in phishing where attackers try to mimic internal or system-generated notation.
No—unless you are certain it matches the provider’s required field format. Typically, email login expects the mailbox address (the actual address) rather than an appended “.login” label. If you’re uncertain, open the provider manually (official site) and enter only the address portion.
Confirm the sender domain, verify the URL/domain of the page where you are being asked to authenticate, ensure you are on the official provider interface, and verify that authentication prompts align with your expected MFA flow. Avoid relying on urgency cues alone.
Immediately change the password (from the official provider site), enable or verify MFA, revoke active sessions if your provider offers that option, and review mailbox rules and forwarding settings for unauthorized changes. If it’s a work account, notify your IT/security team to start an incident response, and consider checking other accounts that might rely on the same password.
MFA significantly reduces risk, but it is not a universal guarantee. Attackers can still attempt social engineering, such as tricking users into entering OTP codes into the wrong place, or using compromised devices. Strong MFA combined with safe browsing habits and domain verification is widely recommended and forms a robust layer of defense.
Because phishing and social engineering rely on prompting users to act. Verification practices—using official entry points, checking correct domains, and avoiding credential entry into unknown forms—reduce the chance that an attacker-created workflow will succeed.
To ground the guidance in recognized practice, the principles described here align with widely used security recommendations from standards and guidance organizations. While the specific wording varies, the common themes are consistent: safe authentication depends on both system design and user verification behavior.
Key principles include:
For authoritative references, you can consult guidance from organizations such as the U.S. National Institute of Standards and Technology (NIST) and security-focused awareness materials from global bodies. NIST guidance on digital identity and general cybersecurity best practices emphasizes that safe authentication requires careful verification, layered defenses, and mechanisms that limit the success of phishing-based user actions.
Even though the content of these FAQs is practical, it is not arbitrary. The core logic follows the same structure found in many security documents: protect credentials, minimize the chance of users entering them in the wrong place, and ensure system design supports safe behavior (for example, by implementing MFA, secure session handling, and clear domain-based trust cues).
The presence of an identifier like [email protected] should prompt caution, not panic. In professional terms, treat any login-related string as a sign to confirm context. Locate the actual mailbox address, navigate to the official provider interface, and complete authentication only where the domain and prompts match your expectations.
By applying the verification steps and conditions above—especially the habit of opening the provider manually rather than using embedded forms—you reduce the chance of falling into login-based scams while maintaining a clean, auditable access process.
Finally, adopt a mindset that treats authentication as a controlled process rather than a click-and-go convenience. Attackers depend on disorder: confusing pages, rushed decisions, and unclear contexts. When you make the login path predictable and verifiable, you remove a major advantage from phishing campaigns and protect both personal and organizational accounts.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
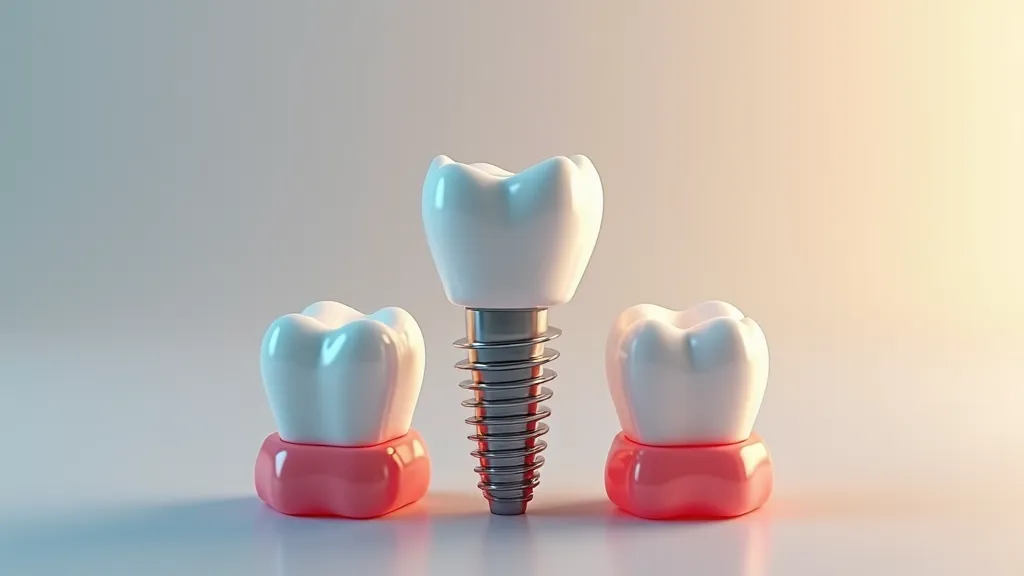
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Understanding 60817674500: Pricing, Supplier Signals, Quality Steps
This guide explains how to interpret the numeric keyword 60817674500 in procurement contexts, how pricing is commonly structured, and what supplier information should be verified before ordering. Objectively, it discusses what such identifiers often represent, why supplier traceability matters, and which due-diligence steps reduce delivery and compliance risk.
822478979788877878878897979797 Buyer’s Guide
This guide explains how to evaluate 822478979788877878878878897979797 procurement decisions with an objective lens. It outlines what the code typically signals in supply-chain workflows, how to verify supplier readiness, and which due-diligence steps reduce risk. You’ll also find a comparison framework, requirements, and practical FAQs for informed purchasing.
PrismaJOY Buying Guide: Requirements, Suppliers, and Pricing
PrismaJOY is a structured solution-focused product guide aimed at helping buyers evaluate sourcing, pricing factors, and implementation readiness. Objectively, PrismaJOY is discussed in terms of how “JOY” features map to selection criteria, compatibility, and supplier support in day-to-day procurement and deployment workflows, emphasizing due diligence and documented requirements.
PrismaJOY Guide: Pricing, Suppliers, and Buying Conditions
This guide explains how to evaluate PrismaJOY for responsible purchasing decisions, focusing on pricing structure, supplier credibility, and practical requirements. Objectively, PrismaJOY is presented as a brand name associated with consumer products, while “supplier” refers to the distribution chain that impacts delivery, warranty handling, and service responsiveness.
How Multishop Streamlines Modern Multi-Vendor Selling
This guide explains how Multishop supports multi-vendor commerce by connecting catalogs, orders, and supplier workflows in a single operational view. In objective background terms, multi-vendor platforms exist to reduce duplication of product and fulfillment management, while improving governance through standardized pricing rules, inventory updates, and supplier controls.
Understanding Gordo9498416253t and Related Product Options
This guide explains how to evaluate Gordo9498416253t-type listings and nearby supply options, focusing on how buyers can verify pricing, supplier credibility, and compatibility before purchase. Objectively, the keyword “Gordo9498416253t” functions as a listing identifier-like term, while “related product options” reflects the broader need to compare sellers, documentation, and performance claims using reliable sourcing and practical checks.