This guide explains how to build a reliable product sourcing and quality control workflow, from supplier selection to verification. Objectively, it covers how sourcing decisions, inspection standards, documentation, and risk management affect outcomes. It also clarifies typical requirements and conditions teams should confirm before placing orders, ensuring operational stability and consistent results across product lifecycles.
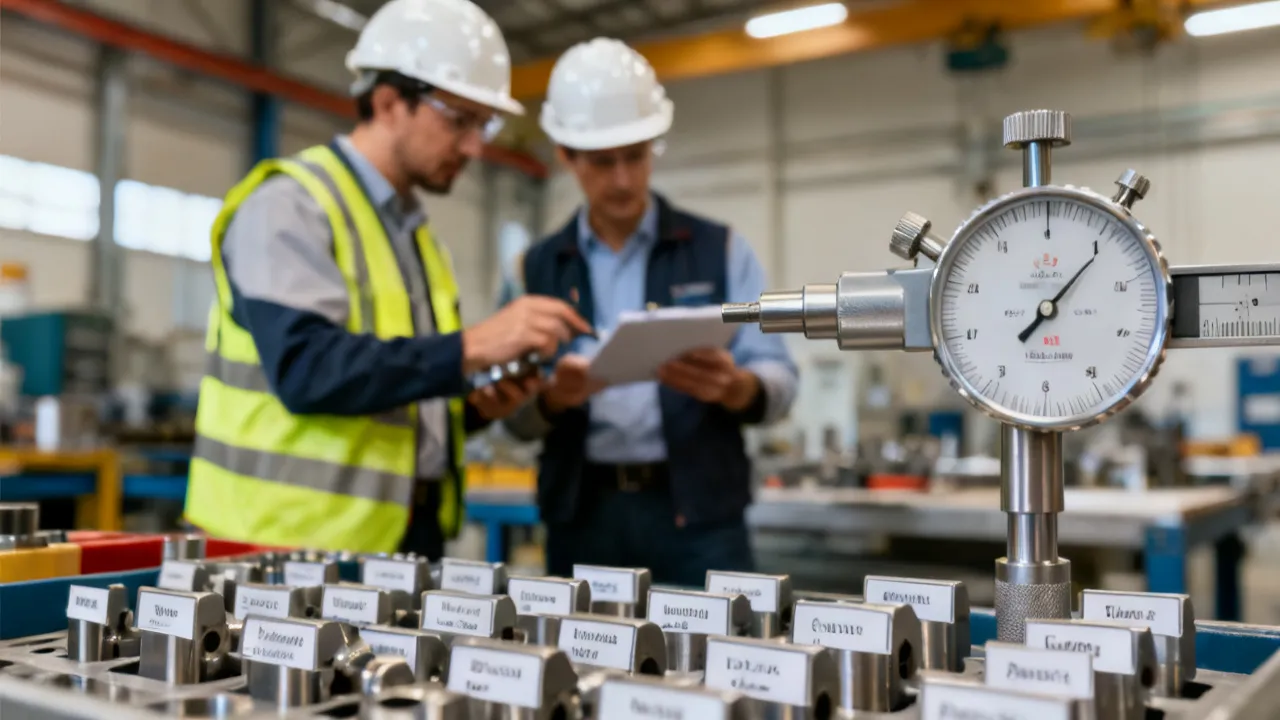
Successful product sourcing is not just about identifying a supplier—it is about creating a defensible system where requirements are clear, inspections are planned, and acceptance is measurable. In practice, professionals evaluating keywords such as '' '' '', Xxx, and '' '' '' typically want the same core outcome: consistent quality, predictable delivery, and documentation that withstands internal audits.
From an industry expert perspective, the highest-risk failures in sourcing programs usually arise from mismatched expectations (specifications not fully translated into supplier processes), weak verification (inspections that do not match critical-to-quality characteristics), and incomplete evidence (records that are unavailable when questions emerge). Therefore, this guide organizes decisions around a verification-minded workflow—selection, contractual requirements, process control, inspection planning, and continuous improvement—so teams can reduce rework and avoid avoidable disputes.
In many organizations, sourcing teams are pressured to move quickly: request quotes, confirm lead times, and place orders. However, “quick” sourcing without verification tends to create hidden downstream costs: expedited freight, scrap, returns, and time lost during investigations. A verification-minded system reduces these costs by making quality expectations explicit before purchase and by ensuring verification activities are mapped directly to what matters most for customer impact, safety, compliance, and functional performance.
To make this actionable, the sourcing system should connect five elements: (1) requirements derived from product intent (including the meaning behind the sourcing keywords), (2) supplier capability to consistently produce against those requirements, (3) inspection and acceptance plans aligned to risk and critical-to-quality characteristics, (4) contract obligations that require documentation and traceability, and (5) feedback loops that drive corrective actions and prevention.
When these five elements are aligned, sourcing stops being a one-time transaction and becomes a repeatable operating capability. That capability is not limited to large enterprises; it is equally relevant to startups, mid-market manufacturers, and service organizations that need consistent outputs from external vendors.
In procurement discussions, terms like Xxx often function as shorthand for one of the following operational themes: (a) a defined product attribute or performance target, (b) a purchasing process step, or (c) a compliance or documentation expectation. Because these keywords may be used differently across organizations, the practical objective is always the same: translate the keyword intent into unambiguous requirements and verification criteria.
When teams say '' '' '' or '' '' '', they frequently refer to constraints—such as material constraints, packaging expectations, tolerance levels, labeling rules, or test evidence. Even if the phrasing differs, the top sourcing outcomes happen when each keyword element is mapped to an internal spec, a supplier capability check, and a measurable acceptance method.
To translate these keywords effectively, teams should assume that the supplier will interpret the words literally and conservatively only if the contract forces it. Many procurement delays occur not because suppliers cannot make the product, but because requirements were not translated into enforceable, measurable criteria. As a result, the supplier might produce a “reasonable interpretation” that is not what the buyer intended, and this creates a mismatch discovered at receiving or even later at customer use.
Therefore, treat keywords as prompts that require structured clarification. A practical approach is to create a keyword “translation matrix,” where each keyword maps to: (1) the exact technical requirement (what is needed), (2) the measurement method (how to verify), (3) the acceptance criteria (what counts as pass/fail), (4) the documentation requirement (what evidence to supply), and (5) the traceability requirement (how to identify which units/lots the evidence refers to).
This translation discipline is particularly important when internal teams use shorthand language. For example, engineering might say “Xxx verified” or procurement might reference “'' '' '' requirements” without clearly stating what the acceptance method is. A verification-minded system compels teams to translate these phrases into measurable obligations so that inspection outcomes are objective and repeatable.
Industry practice starts with requirement clarity. If the requirement is vague, every downstream activity becomes subjective—quotes become incomparable, inspections become inconsistent, and “acceptable” outcomes can drift. Before supplier evaluation, procurement and technical teams should align on:
This requirement-first approach is consistent with widely used quality management principles. It is also aligned with ISO 9001-style thinking: specify what “good” means and manage processes to deliver it reliably. (ISO 9001 is the very referenced international standard for quality management systems; it does not prescribe specific products, but it strongly emphasizes documented, repeatable control.)
Requirement alignment should occur not only at the moment of purchase but also across the lifecycle. For example, if product tolerances change due to engineering revisions, the sourcing system must ensure those revisions propagate into supplier work instructions, inspection plans, and the contract language. Without this, suppliers can continue producing under older interpretations, and buyers can receive shipments that are technically “consistent” with the old documents but not acceptable for current use.
In addition, teams should clarify the scope of responsibility. Some organizations assume the supplier is responsible for meeting all technical requirements, but in practice, certain inputs (like buyer-provided drawings, material grades, or approved sample references) may need to be supplied by the buyer. Clarifying scope reduces disputes later. If an issue arises, both sides can determine whether the root cause was a supplier manufacturing deviation or a missing/incorrect input from the buyer.
Another aspect of requirement clarity is defining what happens when requirements conflict. If a drawing conflicts with a specification or if a procurement keyword suggests a different tolerance than engineering documentation, procurement teams need a precedence rule. For example: “engineering drawing revision takes precedence over all other documents; if no drawing exists, the specification document governs; if conflicts remain, engineering resolves before production.” Defining this prevents suppliers from choosing the most convenient interpretation and then arguing the contract ambiguity.
Finally, teams should incorporate risk assessment into requirement definition. Not all product characteristics require the same level of scrutiny. CTQ classification ensures resources are focused. For example, a minor cosmetic defect might not affect safety but could affect customer perception and brand reputation. Conversely, a functional dimension might directly affect performance and reliability. CTQ decisions help drive inspection strategy and acceptance criteria.
Procurement leaders often ask for “price information,” but price alone cannot predict outcome quality. Industry specialists typically treat quotation review as a combined evaluation of technical feasibility, manufacturing stability, and evidence quality.
Instead of treating price as the main decision variable, teams should analyze:
Where price is involved, it should be evaluated alongside total cost of quality (conformance and nonconformance costs)—a concept often discussed in quality engineering. Nonconformance costs include rework, scrap, returns, customer dissatisfaction, expedited shipping, and administrative overhead.
To evaluate capability objectively, teams should request evidence such as production control plans, inspection coverage, calibration certificates, and prior quality results where available. For certain CTQ-critical items, capability studies might be appropriate. While capability analysis requirements depend on industry standards and risk levels, the key is not to request data “for compliance.” The key is to request data that enables decision-making: Are they capable, are they stable, and can they prove it?
Another common selection failure is confusing experience with capability. Suppliers might have a long history producing related products, but they may have changed processes, equipment, workforce training, or materials. Capability is dynamic. Therefore, selection should include confirmation that their current process environment is consistent and controlled.
Additionally, communication is a capability. If a supplier cannot interpret your requirements, the organization will spend time clarifying before production and may still suffer misinterpretations during output. Requesting a supplier quotation response that includes clarifying questions, documented assumptions, and a structured plan for verification can act as a screening mechanism. When suppliers proactively identify ambiguities and propose verification methods, that is a strong indicator of operational maturity.
Finally, teams should assess their own internal readiness. Even strong suppliers cannot perform reliably if the buyer’s requirements are unclear, if drawings are incomplete, or if specification versions are not aligned. A verification-minded system includes both parties. Supplier selection should not become a blame exercise; it should become a mutual risk alignment process.
Once requirements are defined, teams should convert the sourcing intent (including the keywords) into enforceable supplier obligations. That means the contract or purchase terms should clearly state:
This is also where “conditions/requirements” become operational. Teams should avoid vague phrasing such as “meet quality requirements” without defining measurable acceptance criteria. Instead, acceptance should reference the exact test method and threshold.
Contract language should not only list what the supplier must do, but also specify the consequences of nonconformance and the decision authority for disposition. For example, if a unit fails inspection, who decides whether the lot is rejected, quarantined, reworked, or accepted under concession? Clear authority avoids escalation that can waste time and damages supplier relationships.
To make keyword obligations enforceable, the contract should include a requirement mapping appendix or referenced document set. For instance, if Xxx corresponds to a specific tolerance, the contract should reference the exact drawing revision or specification section. If '' '' '' corresponds to labeling rules, the contract should state the exact label content and formatting and require a labeling verification step.
Another contract detail that often causes failure is timing. Documentation can be required “with shipment,” “within X days,” or “available upon request.” Each timing creates different risks. For receiving inspection, documentation is often needed at the time of intake to perform verification and to ensure traceability. If documentation arrives after receiving without earlier availability, teams might accept product without full evidence, and later disputes can be harder to resolve.
Contract should also define retention. If records must be retained for audits, the contract should specify retention length and storage conditions. Retention ensures traceability evidence is available when questions emerge months or years later.
Finally, incorporate change control explicitly. Suppliers should notify buyers about changes in materials, processes, tooling, inspection methods, or sub-suppliers. The buyer should define whether changes require prior approval or whether notification is sufficient if the CTQ characteristics remain validated. Without clear change control rules, suppliers may implement “continuous improvement” that unintentionally affects quality or evidence availability.
A robust sourcing and quality control workflow uses multiple layers of verification. Experts generally recommend aligning inspection strategy to risk—CTQ characteristics that strongly affect safety, function, or compliance deserve tighter verification.
In practice, a multi-layer workflow helps ensure that failures are detected early and that evidence is collected consistently. A verification system should be documented so that internal auditors can trace how requirements become inspection steps and how inspection results become acceptance decisions.
It is also helpful to define the workflow boundaries. For example: incoming inspection is the buyer’s responsibility up to final acceptance; supplier internal checks are included as part of their control plan; audit activities are part of supplier assurance. When boundaries are unclear, each party may assume the other is doing verification, which leads to gaps.
Additionally, the workflow should specify what happens when defects are detected. A plan that only describes inspections, without describing containment and disposition, is incomplete. Teams should define quarantine procedures, communication steps, document correction requirements, and CAPA expectations.
Incoming checks validate what arrived against the defined requirements. This stage commonly includes:
Incoming inspection should be designed to detect both product quality issues and evidence quality issues. Evidence quality issues include missing certificates, mismatched lot numbers between physical items and paperwork, and incomplete inspection reports. These are not “small admin errors”—they directly reduce the ability to perform root cause analysis if a problem emerges later.
To strengthen IQC, teams should include verification steps for:
IQC is also where organizations can implement sampling logic. Rather than checking everything (which is costly) or checking too little (which is risky), risk-based sampling helps balance cost and confidence. The sampling approach should reference the agreed acceptance method (and potentially statistical sampling standards, where applicable).
When lead times and risk justify it, in-process checks reduce the probability of discovering defects only after full production. The supplier may perform internal checks, while the buyer may specify witness points.
In-process quality control can include monitoring key steps that create CTQ risks—such as material preparation, forming, coating, curing, machining, assembly, calibration, or heat treatment (depending on the product). Witness points are typically used where a failure cannot be easily repaired without affecting quality, or where rework would be expensive or unreliable.
In-process verification is particularly valuable when:
When you specify witness points, make sure the contract and inspection plan specify: what is inspected, at what stage, who performs it, what acceptance criteria apply, and what documentation should be produced. Otherwise, witness points can become mere observation without verification value.
Another best practice is to ensure that supplier internal inspection data is shared in a consistent format. Even if buyers do not perform the tests themselves, they need the records. A supplier might “pass” internally but fail to deliver evidence in a form that buyers can use. If evidence is inconsistent, it is not enough to rely on in-process checks; evidence must be usable.
The final acceptance step ensures that a shipment meets the acceptance criteria. Industry professionals typically insist on:
Final acceptance should not be limited to “physical pass/fail.” It should also confirm that the documentation is correct, complete, and traceable. For example, a certificate may list the correct product name but include a wrong lot number, which undermines traceability.
To implement final acceptance effectively, teams should define release rules. Common release rules include:
Release rules should be consistent across shipments. Inconsistent enforcement often leads to informal overrides and increases risk. A verification-minded system standardizes release decisions so that teams do not accidentally accept product without evidence because of time pressure.
After receiving product, the program should feed findings back into supplier development. If defects appear repeatedly, teams should request a root cause analysis and corrective and preventive actions (CAPA) plan. This turns quality control into a learning system rather than a repeated firefight.
Continuous improvement should include more than tracking defect counts. It should also track:
CAPA should also include verification of effectiveness. Many organizations request corrective action plans but do not confirm that actions improved outcomes. Effectiveness verification might include enhanced sampling, in-process checks, or subsequent batch inspection performance metrics. The goal is to confirm that the root cause has been addressed and that recurrence is reduced.
Supplier development can include training, process adjustments, improved measurement systems, and standardized work. In mature systems, the buyer and supplier jointly refine CTQ definitions, test methods, and inspection plans based on evidence collected over time.
Although the keywords do not explicitly name a city or country, sourcing operations often reflect local manufacturing culture—communication style, documentation norms, lead-time expectations, and typical packaging practices. For teams sourcing from manufacturing hubs, it is useful to anticipate how suppliers interpret:
When working with suppliers near a specific location, teams frequently find that “nearby” suppliers offer quicker iteration cycles, while “farther” relationships may require more extensive upfront documentation. Either way, the verification framework should remain consistent: clear requirements, defined acceptance, and evidence-based decisions.
Localization also affects what “speed” means. Some regions have faster initial quotation cycles but slower documentation turnaround. Others have slower quoting but stronger documentation discipline. A verification-minded sourcing system should anticipate these patterns and define explicit timelines for: quotation clarifications, document submission, sample approvals (if needed), and inspection result delivery.
Documentation language can be another localization concern. Suppliers may provide certificates in a local format, or fields might be translated differently. If you require a specific structure or set of fields, specify them. For example, require: product name, specification revision, lot/batch number, test method, results, pass/fail status, signatory, date, and equipment identifiers (when relevant).
Even measurement tolerances can be interpreted differently if rounding rules are not specified. For example, one supplier may round to the nearest whole unit while another uses one decimal place. When acceptance criteria are based on exact thresholds, rounding differences can cause unnecessary holds and disputes. The contract and inspection plan should specify rounding rules consistent with your internal standards.
Shipping practices can also create nonconformance that appears “product-related” but is actually packaging-related. For example, vibration during transit might crack fragile components, or moisture might degrade materials. If packaging and handling rules are defined in CTQ terms, then shipping-related failures can be traced and corrected. Otherwise, the buyer may mistakenly attribute transit issues to manufacturing defects.
Price information should be treated as a starting point, not the deciding factor. Even when price is competitive, the total outcome depends on how the supplier handles:
To support objective selection, teams can structure quote comparisons with common technical fields: unit price, lead time, tooling charges (if any), minimum order quantity, documentation inclusions, and inspection terms. This ensures the discussion remains anchored to verifiable deliverables.
In practice, “cheap” can be expensive. If a low-cost supplier delivers product with higher defect rates or incomplete documentation, the buyer pays for nonconformance through labor time and operational delays. When buyers calculate total cost of quality, they often discover that selecting the lowest unit price increases cost of goods effectively once rework and dispute resolution are included.
To implement a total cost of quality approach, teams can estimate:
Even when defect rates are unknown, the buyer can use supplier evidence quality as a proxy for risk. Suppliers that provide clear, consistent documentation tend to be more transparent about process control. That transparency can reduce audit friction and improve decision confidence during receiving.
Price comparisons should also account for differences in sampling and inspection coverage. One supplier might quote a low price but propose reduced inspection coverage or exclude documentation deliverables. Another might include additional inspection or stronger evidence as part of their price. Without comparing these technical inclusions, buyers can unintentionally accept “price” that is low only because verification costs were shifted to the buyer.
Additionally, buyers should consider lead time reliability. A supplier with a slightly higher unit price but better delivery predictability can reduce inventory carrying costs and production scheduling disruptions. When lead times are uncertain, buyers can incur costs through overtime, downtime, and increased safety stock. Therefore, “price information” should include delivery performance as a component of cost evaluation.
Below is a supplemental, practical framework. It compares common sourcing-and-quality approaches, then summarizes credible sources and a step-by-step plan. No links are included.
| Category | Approach | Strengths | Limitations |
|---|---|---|---|
| Supplier verification | Capability and evidence review before ordering | Reduces risk early; aligns expectations | Requires upfront effort from technical teams |
| Inspection strategy | Risk-based CTQ sampling and defined acceptance criteria | Focuses resources on what matters very | Needs clear CTQ definitions and test methods |
| Documentation control | Documented deliverables tied to lot/batch traceability | Supports audits and faster dispute resolution | Can slow shipments if formats are unclear |
| Nonconformance management | Structured CAPA with root cause and prevention | Improves good supplier performance | May require governance and escalation routines |
| Ongoing confidence | Performance tracking and periodic requalification | Detects drift over time | Needs consistent receiving data and governance |
While these references are widely discussed in quality and sampling contexts, organizations should always ensure that the sampling standard selection matches their risk profile, regulatory expectations, and internal policies. In some industries, different national or customer-specific standards may apply. The goal is not to pick the “most famous standard,” but to ensure that sampling and inspection decisions are justified and consistent with your acceptance logic.
To add operational rigor, consider establishing internal templates for each step. For example: a requirement translation template, a supplier evidence request checklist, an inspection plan template that lists CTQ characteristics and sampling rules, and a nonconformance form that records lot numbers, defect categories, containment actions, and requested CAPA documentation. Templates reduce variability and ensure that evidence collection remains consistent across teams and time.
It is also useful to confirm the practical “execution conditions.” For instance, if your inspection plan requires specific equipment at the supplier (like gauges, profilometers, spectrometers, coordinate measuring machines), specify whether that equipment is required to be used and whether calibration records must be shared. If supplier measurement equipment is not controlled, acceptance results become less trustworthy, even if the test method is correct in theory.
Similarly, clarify the “operational definition of a lot.” Suppliers might define a lot based on production shift, machine run, or material procurement batch. Buyers should specify the lot basis that aligns with traceability needs and acceptance logic. Without a consistent lot definition, it becomes difficult to isolate problems and it becomes easier for disputes to emerge.
Treat them as intent placeholders rather than final requirements. The top practice is to map each keyword to measurable CTQ characteristics, define acceptance criteria, and confirm the supplier can test and document those characteristics using the agreed methods.
No. Price is important, but it should be evaluated alongside supplier capability, evidence quality, inspection plans, lead-time reliability, and the expected cost of nonconformance. A slightly higher unit price can be rational if it materially reduces defect rates and rework.
Look for evidence of process control (not only claims), measurement readiness, traceability practices, prior performance with similar products, responsiveness during issue resolution, and willingness to follow documented verification steps.
Use risk-based CTQ thinking. Define which characteristics can cause safety, functional, compliance, or customer-impact failures, then set sampling intensity and acceptance thresholds accordingly. As historical performance improves, inspection can often be adjusted while still maintaining audit-ready documentation.
Define a prior rule in the requirements. Commonly, teams place the shipment on hold, verify traceability with the supplier, and require corrected documents before release—because mismatches weaken the ability to investigate and isolate root cause.
Requalification frequency depends on risk and historical performance. Higher-risk products or repeat issues typically require more frequent reviews. Use performance tracking metrics and trigger-based reassessment when drift indicators appear (e.g., rising defect categories, incomplete documentation, or repeated nonconformance).
Yes. ISO 9001 emphasizes process control, documented evidence, corrective actions, and continual improvement—principles that directly support reliable supplier sourcing and consistent verification discipline.
In many real procurement programs, the very expensive failure is not a single defect—it is the inability to prove whether defects are systemic. When teams lack defined CTQ mapping for keywords like Xxx or when supplier obligations are not translated into verifiable contract language, investigations become subjective. Disputes then escalate because neither side can reference an agreed standard for what “acceptable” means.
To prevent this, experts recommend ensuring every critical requirement is tied to at least one of the following: (1) a measurable test, (2) a documented inspection record, or (3) a traceability evidence artifact. When evidence exists, decisions become more objective and less personal.
There are other “subtle failures” that frequently occur even when teams appear to be doing the right things. Examples include:
These failures highlight that verification is not only about the test itself. Verification is also about traceability, documentation, and repeatability of decisions. A good procurement outcome requires a “system” rather than isolated steps.
When experts review sourcing programs, they often find that the best improvement opportunities are in the “interfaces” between functions—engineering-to-procurement translation, procurement-to-contract translation, contract-to-supplier execution, supplier execution-to-documentation delivery, and receiving-to-decision enforcement. Each interface is a potential gap where ambiguity can slip in.
Thus, a verification-minded workflow must assign accountability at each interface. For instance, engineering is accountable for defining CTQ characteristics and test methods; procurement is accountable for converting them into contract language and ensuring evidence deliverables are listed; quality teams are accountable for enforcing receiving inspection and release rules; and supply chain governance is accountable for tracking performance and requalification triggers.
Because the prompt does not define specific products, the following examples describe typical verification logic that teams can adapt to their context:
It can also help to consider “negative examples”—what happens when teams skip verification thinking. For instance, if a dimension tolerance is specified but the supplier’s measurement system is not calibrated, measurement uncertainty can cause false acceptance or unnecessary rejection. If acceptance criteria are defined but the supplier uses a different measuring instrument or rounding approach, pass/fail decisions can differ between supplier and buyer.
Similarly, if packaging requirements are not defined in measurable terms, damage during transit may be treated as a random occurrence. But if packaging CTQ includes drop test validation, moisture resistance, and label durability requirements, then transit issues can be investigated with a clearer causal path. This leads to more durable resolution and fewer repeat incidents.
For documentation CTQ, skipping detailed requirements often results in paperwork that is technically correct in general but incomplete in traceability. For example, a certificate might list product type and specification but not include the equipment ID, date, or lot number. During an audit or customer complaint, such a certificate might not support the investigation. Therefore, documentation requirements should include evidence usability details, not only document existence.
Quality control should not be treated as a purely defensive activity. Over time, the very mature procurement organizations use the data collected from inspections and customer feedback to improve both:
As a result, purchasing teams gain stronger leverage and suppliers gain clearer expectations—reducing cycle time for approvals and disputes.
To integrate continuous improvement, teams should implement structured supplier performance reviews. These reviews can include: defect rates by category, documentation completeness rates, on-time delivery performance, and summary of nonconformance trends. When reviews are structured and evidenced, they encourage constructive improvement rather than blame.
Additionally, buyers can support supplier development by providing clear feedback and by sharing internal standards for what “good evidence” looks like. For example, buyers can show sample certificates that include required fields and correct lot traceability. Buyers can also clarify preferred formats and file naming conventions that make document review efficient.
Supplier development can include joint problem-solving workshops for recurring CTQ issues. When recurring issues exist, it is often because the supplier’s process controls are not addressing the root cause. Joint sessions help align the buyer’s understanding of the problem with the supplier’s view of process conditions. This alignment can accelerate corrective action effectiveness.
Finally, continuous improvement also includes improving the buyer’s own system: refining keyword translation rules, updating inspection plans based on performance, and ensuring contract documents remain synchronized with engineering revisions. Continuous improvement is not limited to the supplier.
Keywords such as '' '' '', Xxx, and '' '' '' are top understood as prompts for requirement translation, not as final specifications. When teams integrate supplier selection with contract-defined obligations, risk-based inspection, and evidence-based acceptance, sourcing becomes a repeatable operational capability rather than a one-off procurement event. If you standardize the workflow—requirements first, capability checks next, verification plans defined, and continuous improvement built in—your outcomes become more predictable across product lifecycles.
To make the takeaway operational, it helps to remember that verification is built from three pillars:
When these pillars are present, sourcing decisions become defensible not only during day-to-day operations but also during audits and customer escalations. In other words, the organization’s quality story becomes evidence-backed rather than assumption-based.
Adopt a “keyword-to-spec” translation step. Convert each keyword phrase into a structured requirement: what is required, how it is measured, what the acceptance threshold is, and what evidence must be supplied.
Additionally, consider implementing a formal requirement review gate before issuing purchase orders. This gate can require cross-functional sign-off (engineering/quality/procurement). The review should confirm that each keyword is not only interpreted but also converted into verifiable clauses in the contract or attached specification documents.
In very professional procurement settings, buyer verification remains important—at least for CTQ characteristics or higher-risk items. Supplier self-inspection can be a component, but relying exclusively on it typically reduces transparency and weakens audit readiness.
Supplier self-inspection can be useful when the supplier has strong process control and a proven history. However, the buyer still needs receiving inspection or alternative verification to confirm that the supplier’s controls are working for the specific lots being delivered. Self-inspection can be impacted by short-term process changes, equipment drift, or workforce transitions that are not visible to the buyer.
Recurring issues often result from unclear requirements, inadequate process controls at the supplier, measurement system problems, insufficient training, or change-control gaps where materials or settings drift without timely notice.
Recurring issues can also emerge when CAPA is not effectively verified. A supplier might implement actions that improve documentation but do not actually correct the process. Or the supplier might correct the issue for one lot but not standardize the change so it persists over time. Verification of effectiveness—through enhanced sampling, monitoring, or updated process controls—is essential to prevent recurrence.
Finally, recurring documentation nonconformance can occur when requirements are stable but the supplier’s documentation processes are not. For example, if labels are generated by a software system or if certificates are templated, a recurring mismatch might reflect a systematic issue in data mapping rather than a physical defect. Treat documentation nonconformance with the same seriousness as physical defects, because it affects traceability and audit integrity.
Define escalation conditions in advance: timeframes for response, required evidence in nonconformance cases, interim containment steps, and decision authority for hold/release actions.
Escalation structure should include “decision points.” For instance: if the supplier does not provide containment evidence within a defined timeframe, the buyer triggers a hold status and requests immediate corrective action verification. If root cause analysis is not provided within a defined timeframe, the buyer might increase inspection intensity or initiate supplier requalification activities.
Escalation should also specify what “response” means. A response that says “we are investigating” without delivering evidence or timelines is not a valid response in most mature quality systems. The escalation plan should require: containment details, interim inspection results, affected lot identification, and a CAPA schedule with measurable milestones.
Not necessarily for every case, but it is generally prudent to verify effectiveness. Reinspection or enhanced sampling can confirm that corrective actions improved outcomes rather than just addressing documentation.
Effectiveness verification should be risk-based. For high-risk CTQ issues, reinspection is typically required. For low-risk or isolated documentation issues, a lighter verification approach might be sufficient if the supplier demonstrates process corrections in evidence. In all cases, effectiveness verification should include both physical quality outcomes (defect rates) and documentation/tracing outcomes (certificate completeness and traceability consistency).
The core logic is industry-agnostic: translate intent into measurable requirements, verify using agreed sampling and methods, and manage nonconformance with root cause and prevention. The CTQ details and test methods vary by product category, but the verification discipline remains consistent.
For regulated industries (such as medical devices, aerospace, or other compliance-heavy sectors), the verification framework becomes even more important because documentation and traceability are not optional. In such environments, contract language and evidence deliverables often need to align with customer or regulatory expectations. Even in non-regulated industries, customers and internal auditors still expect defensible evidence for quality decisions.
In services and non-manufacturing contexts, the same verification logic can apply. For example, CTQ characteristics might relate to timeliness, completeness of documentation, or adherence to process controls. Suppliers might be service providers, and evidence might include logs, reports, and audit trails. The “keyword-to-spec” translation remains the same concept: convert intent into measurable acceptance criteria and ensure evidence supports verification.
Urgency should not remove verification discipline; it should change how you apply it. Instead of skipping verification, scale it appropriately:
Urgent procurement often results in decisions made with incomplete evidence. A verification-minded framework reduces that risk by prioritizing the most critical evidence first, ensuring that “fast” does not become “unverifiable.”
Change control must be explicit. You should require a formal change notice, specify which CTQ characteristics are impacted, and confirm that the supplier can continue producing under the revised requirements without violating evidence and traceability rules.
Operationally, you can require: an engineering change record (or equivalent), updated drawings/specifications revision identifiers, supplier confirmation of impact assessment, and agreement on whether requalification or enhanced sampling is needed. For traceability, ensure that lots produced under the previous revision are clearly identified, and define whether they are eligible for acceptance or must be rejected or reworked.
Common metrics include defect rates by category, documentation completeness, traceability match rate, on-time delivery, and recurrence rates of nonconformance. Additionally, track the time-to-containment and time-to-CAPA closure, since responsiveness is part of verification effectiveness.
For evidence quality, measure how often documentation is missing, mismatched, or incomplete at receiving. Documentation defects can be more frequent than physical defects, and yet they can still cause holds and prevent confident release. Measuring documentation performance encourages supplier improvement in evidence discipline, not only in physical manufacturing.
Supplier evidence packages should be tailored to risk, but typically include: capability evidence for CTQ characteristics, calibration certificates or evidence of measurement system readiness, inspection/test procedures or control plans, sample inspection records (if applicable), traceability process description, and documentation examples that match your required format.
For nonconformance management, request an example CAPA report or outline of their problem-solving approach (root cause method, containment process, and prevention strategy). The objective is not to collect documents for their own sake; it is to ensure you will have usable evidence at the time of inspection and acceptance.
Consistency improves when both parties use the same test methods and when measurement system readiness is confirmed. Where feasible, conduct measurement alignment activities such as:
Even when test methods are identical in writing, interpretation differences can occur. Aligning interpretation early improves reliability of acceptance decisions and reduces recurring disputes.
Acceptance criteria drift occurs when requirements are informally adjusted due to operational pressure. Prevent it by:
Acceptance criteria drift undermines audit readiness and creates inconsistent product quality outcomes. A verification system must treat acceptance criteria as controlled documents.
A minimum viable framework can include:
Even a lightweight framework can prevent many common sourcing failures when it is applied consistently and documented clearly. As the organization matures, you can add more advanced sampling logic, in-process witness points, and deeper supplier qualification processes.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
The Guide to Car Trading
Understanding the Costs of Hiring Lawyers in 2025
Concerned about the expenses associated with hiring a lawyer in 2025? Discover how to manage legal costs and locate cost-effective legal representation with our detailed guide.
Finding Financially Feasible Senior Apartments
As we enter our golden years, finding a home that not only meets our comfort and accessibility needs but also fits within our budget becomes a critical concern.
Understanding the Concept of Psemc Fnas
This article delves into the emerging theoretical framework of Psemc Fnas, a concept gaining attention in academic circles for its potential to reshape existing paradigms. Psemc Fnas relates to theoretical constructs that challenge traditional methodologies, suggesting new directions for research and experimental design. Understanding its fundamentals could pave the way for innovation in multiple disciplines.
Discovering the Secrets of Cassia Carniel
Cassia Carniel, an intriguing subject in botanical studies, offers a wealth of knowledge on plant life and ecological contributions. This comprehensive analysis explores its botanical characteristics, potential applications, and ecological significance, providing insights into its role in both natural and human-made environments.
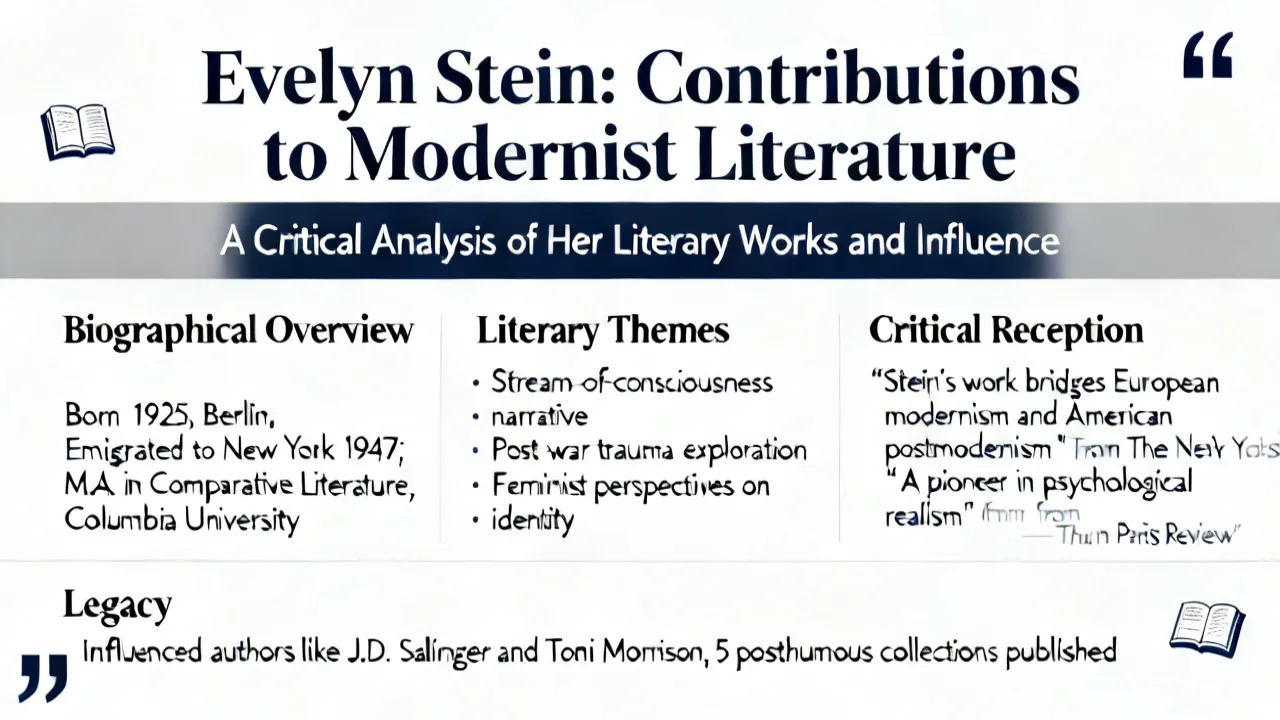
Delving into Evelyn Stein's Literary Influence
This guide explores the profound literary influence of Evelyn Stein. Evelyn Stein is a celebrated figure known for her contributions to contemporary literature. Her works have been influential in shaping modern narrative techniques and exploring complex themes. This article provides an in-depth analysis of her impact and significance in the literary world.
Stefan Ligocki: A Scholar's Influence
This article delves into the impactful career of Stefan Ligocki, a respected academic known for his significant contributions to his field. Through exploring his academic endeavors and scholarly work, we gain insights into how Ligocki's research has influenced contemporary thought and practice. Highlighting key aspects of his career, this comprehensive analysis illustrates his role in shaping modern academic discourse.